Senior Cyber and AI Governance Expertise
Independent vCISO, ISO 27001 and ISO/IEC 42001 audit, and AI governance for organisations across Australia and the world, delivered directly or as part of your team.
Book a Consultation CallEnterprise Resilience
Modern risk is interconnected. We protect your business across the three critical domains of the digital age.

From AI
AI is now embedded across business operations, delivering efficiency but introducing new risks. Organisations must protect sensitive data fed into models and ensure ethical governance. We help you take a deliberate approach to AI, ensuring risks are identified, managed, and aligned with evolving regulations.
From Cyber
Cyber risk is driven by sophisticated threat actors and rapid technological change. Any organisation that relies on digital systems is exposed. Mitigation isn't just about complex technology; it starts with clear policies, sound governance, and a culture of risk-aware decision-making.

From IT
IT risk evolves as systems become more interconnected. Understanding the specific operational risks facing your business, from legacy systems to third-party dependencies, is essential. We implement robust frameworks to ensure your technology is resilient, compliant, and reliable.
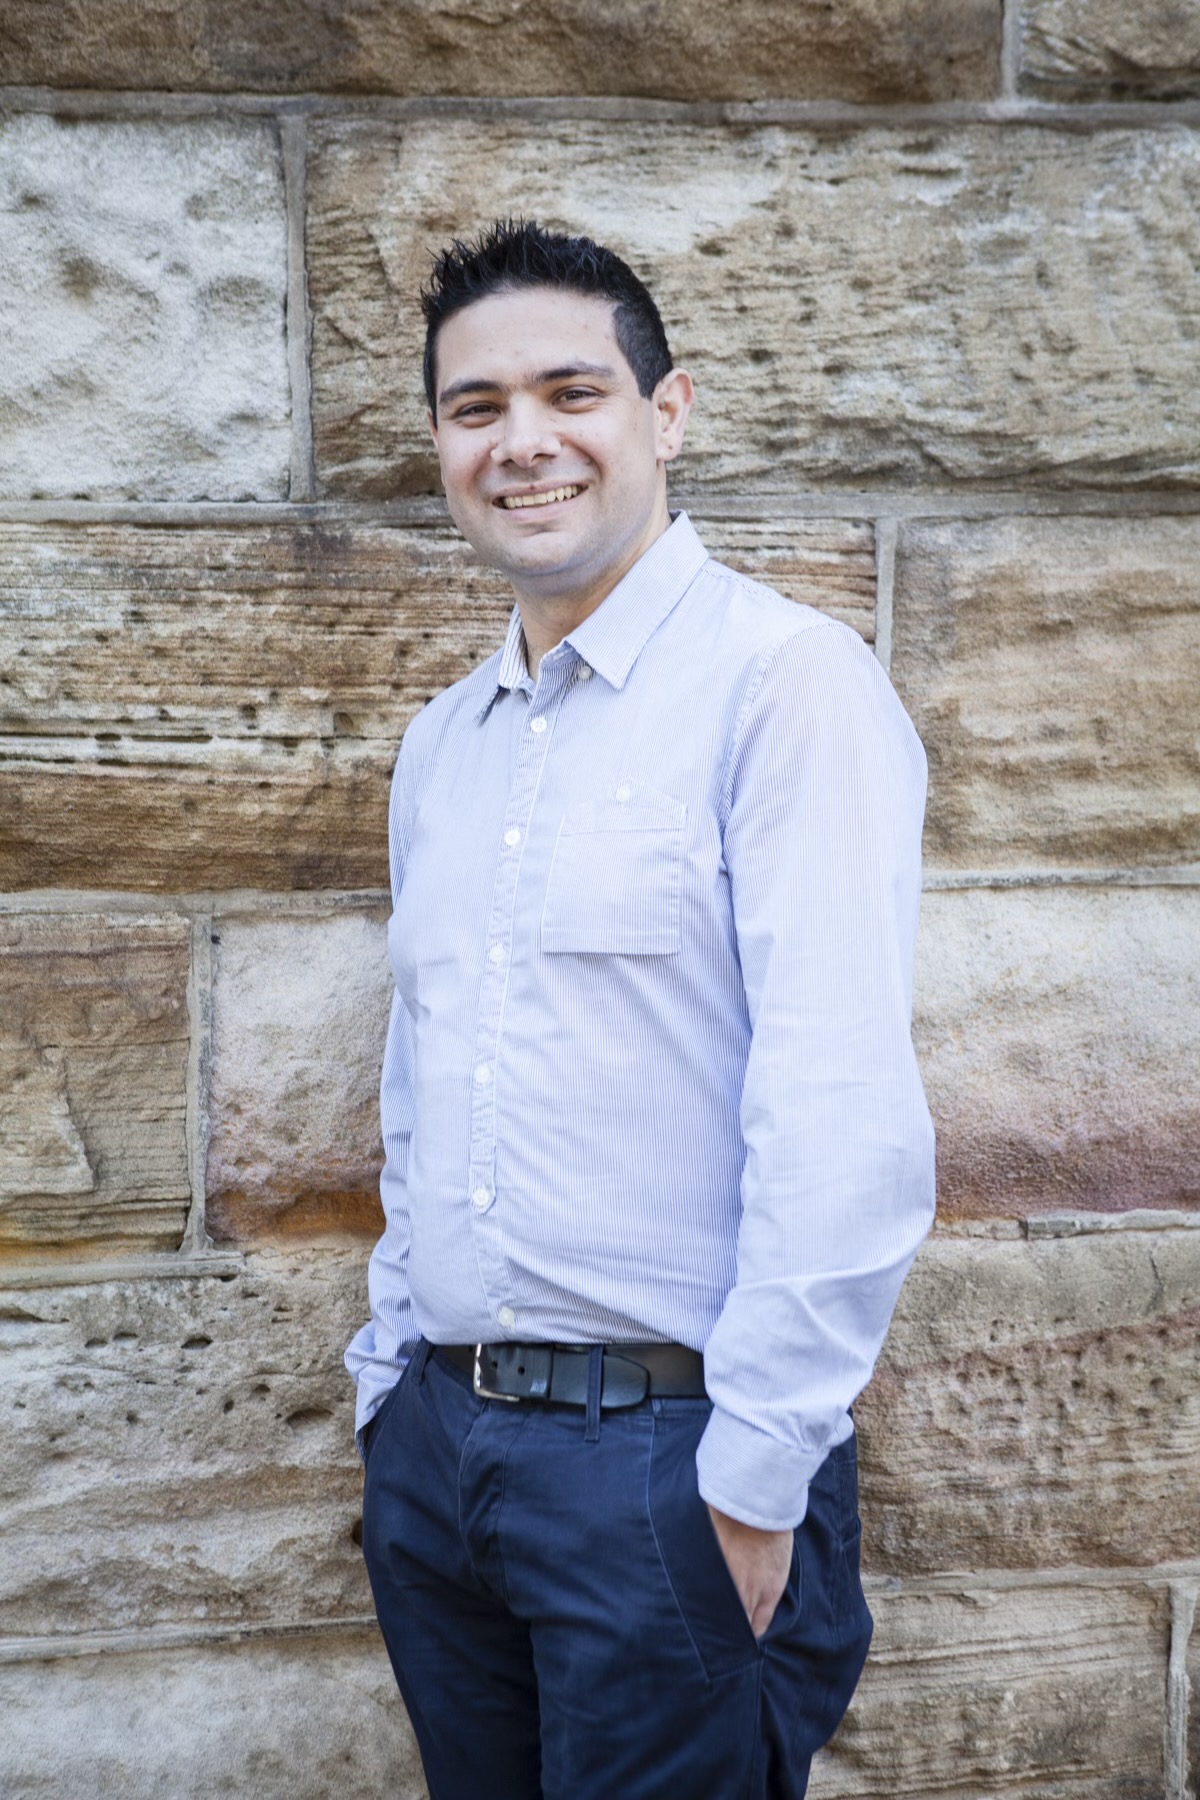
Joe Cozzupoli is an independent cybersecurity and AI governance adviser and founder of Silver Lining Cyber. He works as a vCISO, auditor and adviser, directly and through consulting partners. Recent work includes ISO 27001 and ISO/IEC 42001 internal audits for an accounting firm, a board-endorsed security roadmap for a mining divestiture, and cyber assurance for a major rail programme.
Joe began his career in network and data centre architecture at Optus and Cisco, then held senior security roles at Palo Alto Networks, Citrix and Microsoft, followed by technology risk and cyber work for financial services and healthcare clients at KPMG. He writes for CSO Online, the ISMG network and ISACA Journal, holds ISO/IEC 42001 Lead Auditor, CISSP, CISM and CCSP certifications, and is President of the Global Council for Responsible AI (GCRAI) Australia Chapter.
Core Capabilities
Right-sized services that support the sustainability of your security program.
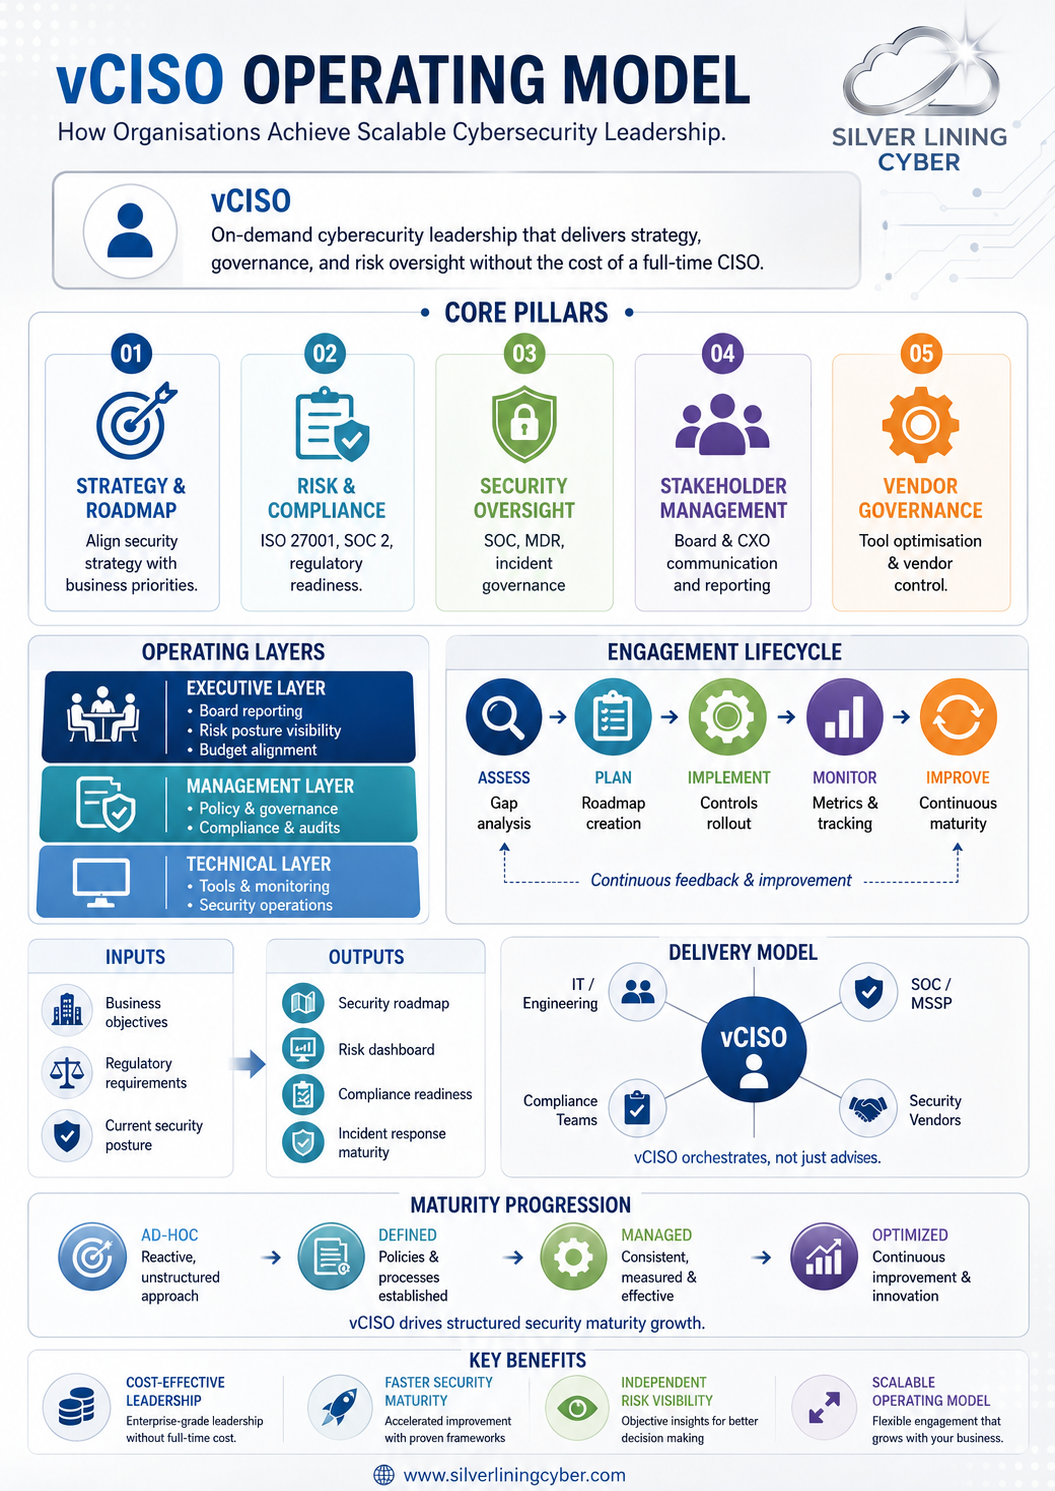
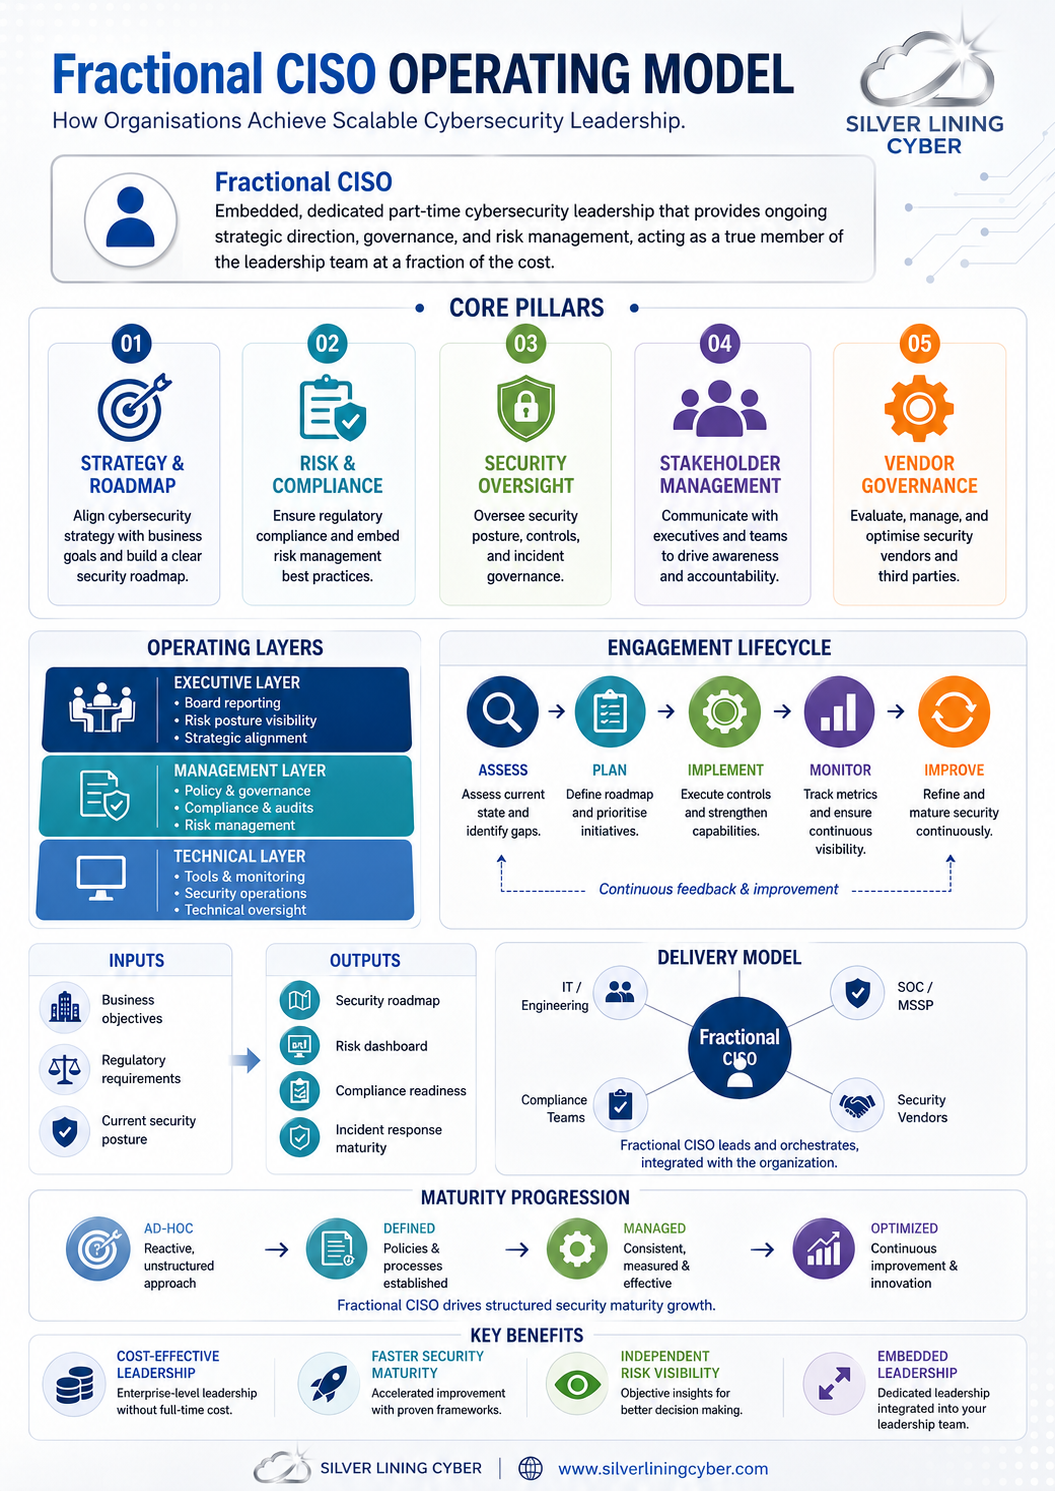
Virtual & Fractional CISO
- Cybersecurity Strategy & Roadmap Development
- Strategic Advisory
- Executive & Board Reporting
- Security Program Maturity Assessments
Governance, Risk & Compliance
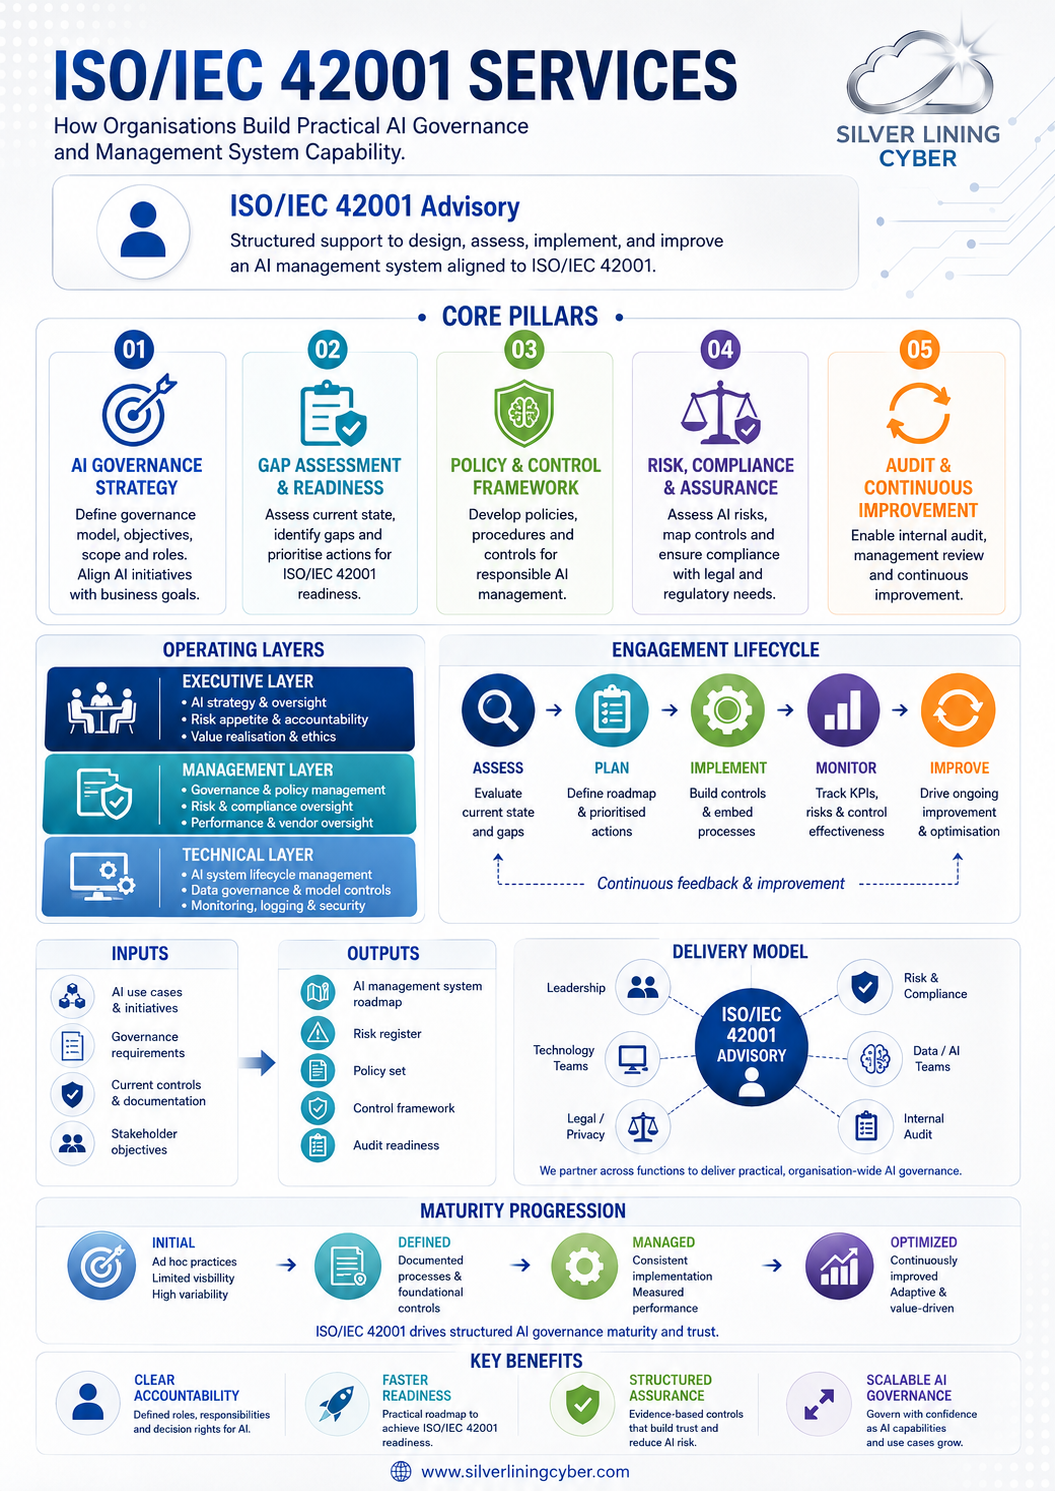
- ISO/IEC 42001 Readiness & Advisory
- ISO/IEC 27001 Readiness & Advisory
- NIST, ASD Essential 8, SOCI & APRA Alignment
- Risk Management Framework Implementation
- Enterprise Security Architect
Strategic Advisory & Enterprise Growth
- C-Suite Engagement Support
- Executive Messaging & Value Narrative
- Strategic Account & Stakeholder Mapping
- Procurement & Risk Conversation Support
- Competitive Positioning & Objection Handling
Technology Assurance
- Security architecture reviews and threat modelling
- Cloud security posture and secure design
- Third-party and supply chain risk assessments
- Zero Trust architecture strategy
- Identity and Access Management (IAM) governance

Trusted by Industry Leaders
"Joe has always been great. We worked together for a few years. He has always been an industry thought leader, assisted in finding the best solutions and been an incredible partner wherever he has landed."
"Joe is a Virtual CISO who consistently delivers exceptional value for clients. He has a strong ability to translate complex cybersecurity and technical initiatives into clear, measurable business outcomes, ensuring security strategy aligns with risk, governance, and organisational priorities."
"Joe combines deep cybersecurity expertise with the confidence and clarity to engage senior executives. He connects security risks with business priorities and practical action. I strongly recommend him for Field CISO and executive security advisory engagements."
Let's Connect
Ready to discuss your security strategy, AI governance, or fractional leadership needs? Schedule a time directly on my calendar for a consultation call.
Book a 30-minute conversation